Build on the record. Check it from your own systems.
Everything people do in HONESTAS, your systems can do through the API, with the same permissions, walls and records. Read and verify sealed records, receive events as they happen, link your partners' agents and put a quote journey on your own site.
POST ‹the verify endpoint›
Content-Type: application/json

{ "file": "2026-1020-7741.json" }

// 200 OK
{
  "verdict": "holds",
  "records": [
    { "id": "2026-1009-7741", "seal": "matches" },
    { "id": "2026-1015-7741", "seal": "matches" }
  ],
  "timestamp": "checks",
  "countersigned": "2 of 2",
  "newer_versions": ["starting-table"]
}One record, in an open format you can read.
Every sealed decision is one JSON document, and a Decision Passport is a file of them. The format is published, so your systems, your auditor and your partners read the same thing we do.
- Who decided, under which authority and version
- Every piece of evidence with its own fingerprint
- The tables and wordings it was pinned to
- The seal, the outside time stamp and the countersignatures
{
  "record": "2026-1015-7741",
  "kind": "claim.settlement",
  "owner": { "firm": "northgate", "unit": "claims" },
  "decision": { "outcome": "settle", "amount": 930000, "currency": "GBP" },
  "signed_by": "sara.lindqvist",
  "authority": { "instrument": "CA-ASH-01", "version": 2 },
  "checks": { "second_model": "agree", "passed": 27 },
  "evidence": [
    { "item": "roof-photographs", "fingerprint": "sha256:7c1e04a9…" }
  ],
  "pins": [{ "table": "starting-table", "version": 3 }],
  "seal": { "fingerprint": "sha256:f0f668bf…", "countersigned": 2 }
}
A sealed claim record, shortened
Check a record without asking us.
Send the file to the verify endpoint, or run the published verifier library on your own machines with no call to HONESTAS at all. Both give the same three verdicts. Sandbox access comes with the exact addresses and the library for your language.
- holds
Every fingerprint matches its seal, the time stamp checks and the countersignatures are present.
- changed
Something in the file differs from what was sealed. The answer names the record and the part, with the code
HASH_MISMATCH. - holds, newer version
The record is intact, and a table or wording it was pinned to has been replaced since.
// the published verifier library, installed on your own machine
const file = await readFile("2026-1020-7741.json");
const result = await verifier.verify(file);

// nothing is sent anywhere
console.log(result.verdict);   // "holds"
The verifier library, offline
Everything that happens, in order, from where you left off.
Read events in order from your last position, filtered by type. Each event carries the record it belongs to, so your systems can fetch the full record when they need it.
record.sealedrefusal.recordedroom.openedruling.signedpayment.heldpassport.issuedrecord.supersededcall.handed_over
GET ‹the events endpoint›
    after: evt_8841
    types: record.sealed, refusal.recorded

// 200 OK
{
  "events": [
    { "id": "evt_8842", "type": "refusal.recorded",
      "code": "GATE_DISAGREEMENT", "case": "CLM-2026-5120" },
    { "id": "evt_8843", "type": "record.sealed",
      "record": "2026-1015-7741" }
  ],
  "next": "evt_8843"
}Your systems hear it the moment a record is sealed.
Choose the events for each endpoint. Every delivery is signed, so your systems can trust it, and a failed delivery is retried and explained on the endpoint's own page.
- Signed with a secret only your endpoint holds
- Retried, in order, until your endpoint answers
- Each delivery shows what was sent and what came back
const sig = req.headers[SIGNATURE_HEADER];   // named on the endpoint's page
const ok = checkHmac(rawBody, sig, ENDPOINT_SECRET);
if (!ok) return res.status(401).end();

const event = JSON.parse(rawBody);
if (event.type === "record.sealed") {
  await claims.attachRecord(event.record);   // your own system
}
Check the signature first
Your partners' agents talk to yours, under a written agreement.
Brokers, coverholders and reinsurers connect their AI agents to yours over the open Agent2Agent protocol. Each link names the agreement it works under and what each side may ask.
- Every request is signed by the agent that sent it
- Only the skills the agreement allows, nothing else
- A request outside the agreement is refused and recorded
- Each exchange kept on both firms' records
{
  "name": "Northgate Mutual · bordereaux",
  "url": "https://agents.northgate.example/bordereaux",
  "agreement": "CA-118",
  "skills": [
    { "id": "bordereau.submit" },
    { "id": "claim.status" }
  ],
  "auth": "signed request, one key per partner"
}
An agent card, published per partner
A quote journey on your site, with the disclosures locked in.
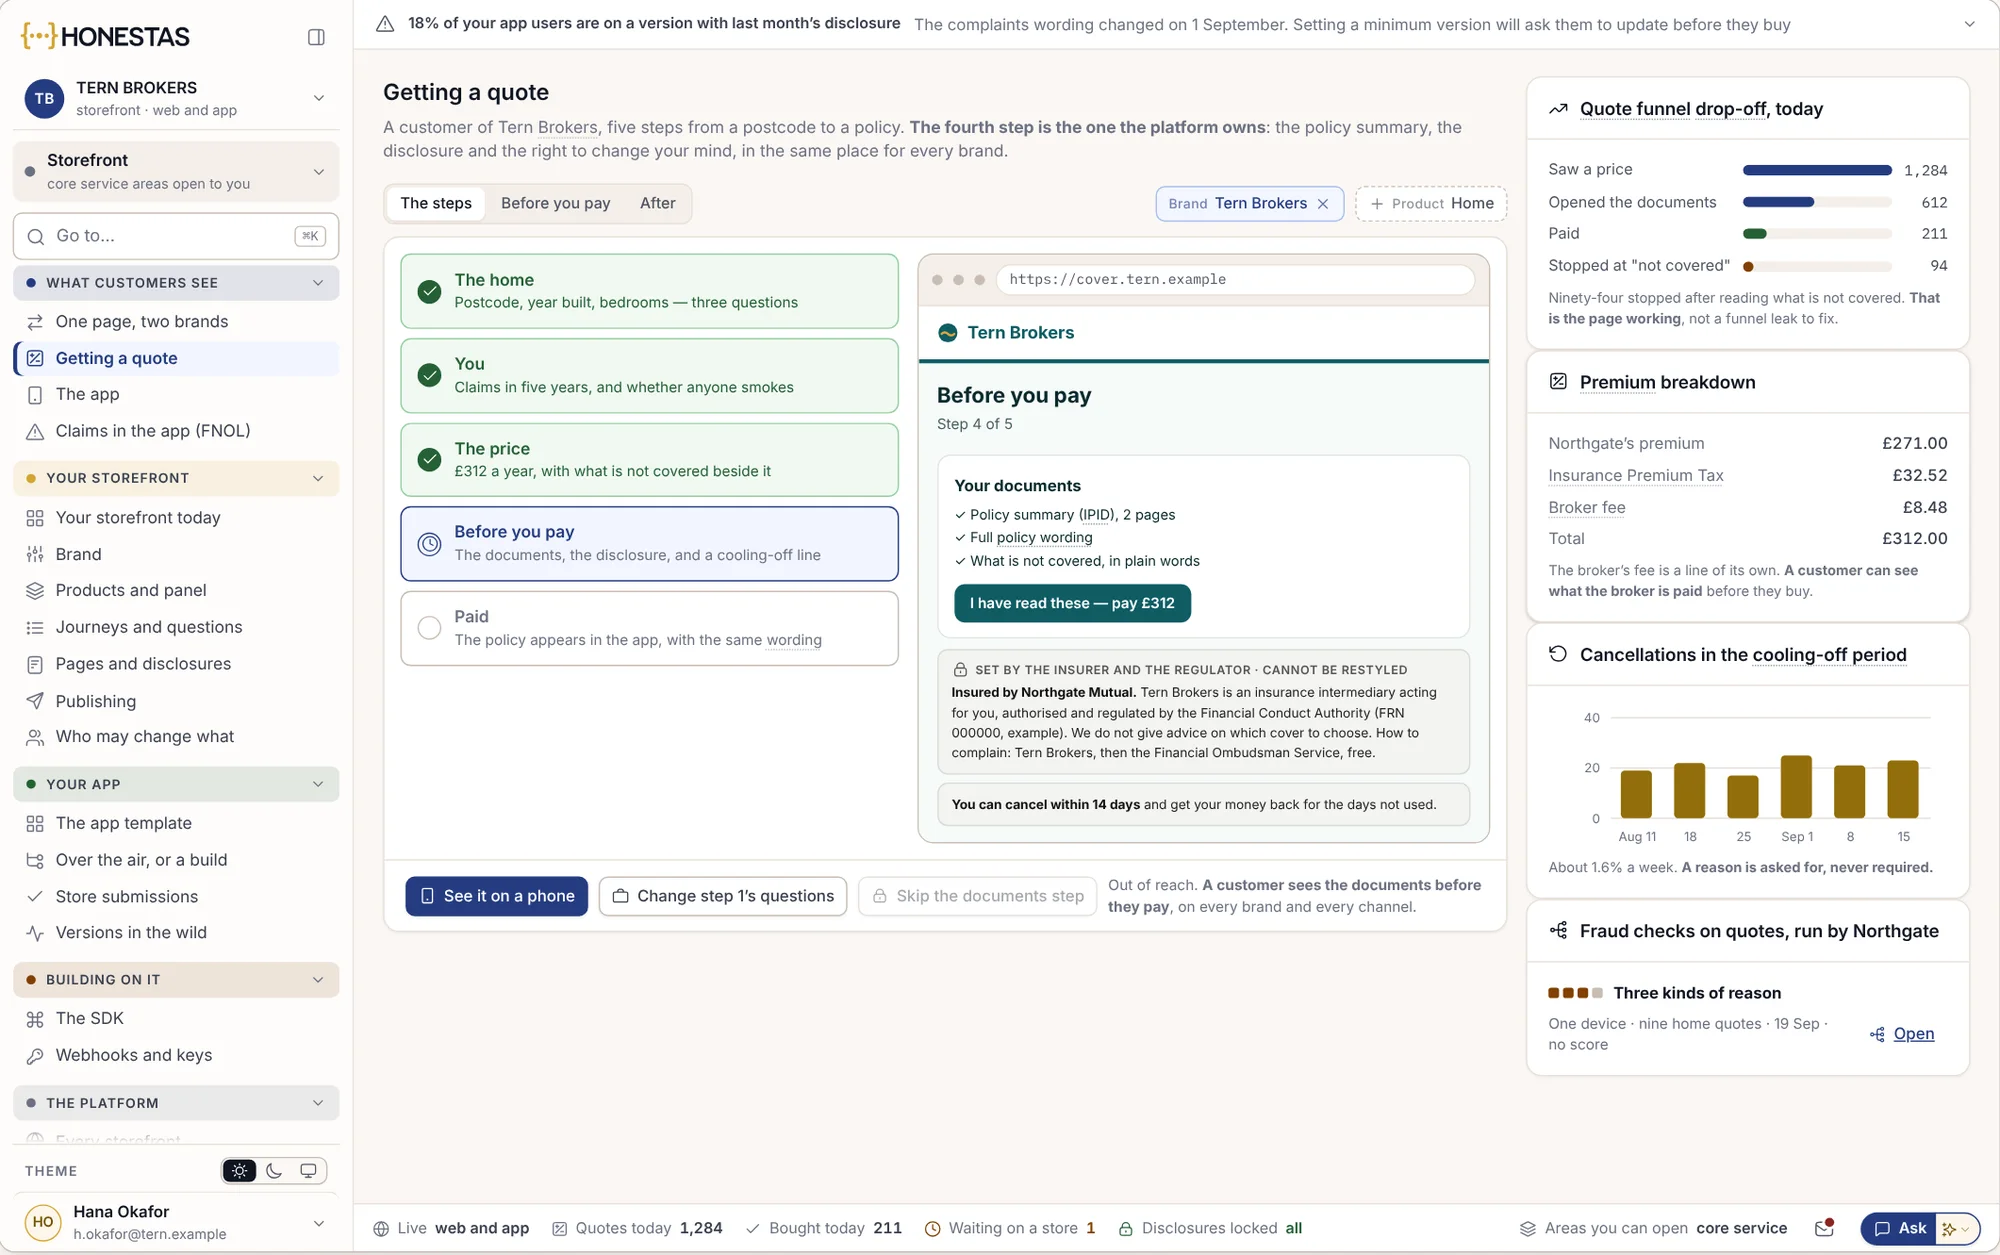
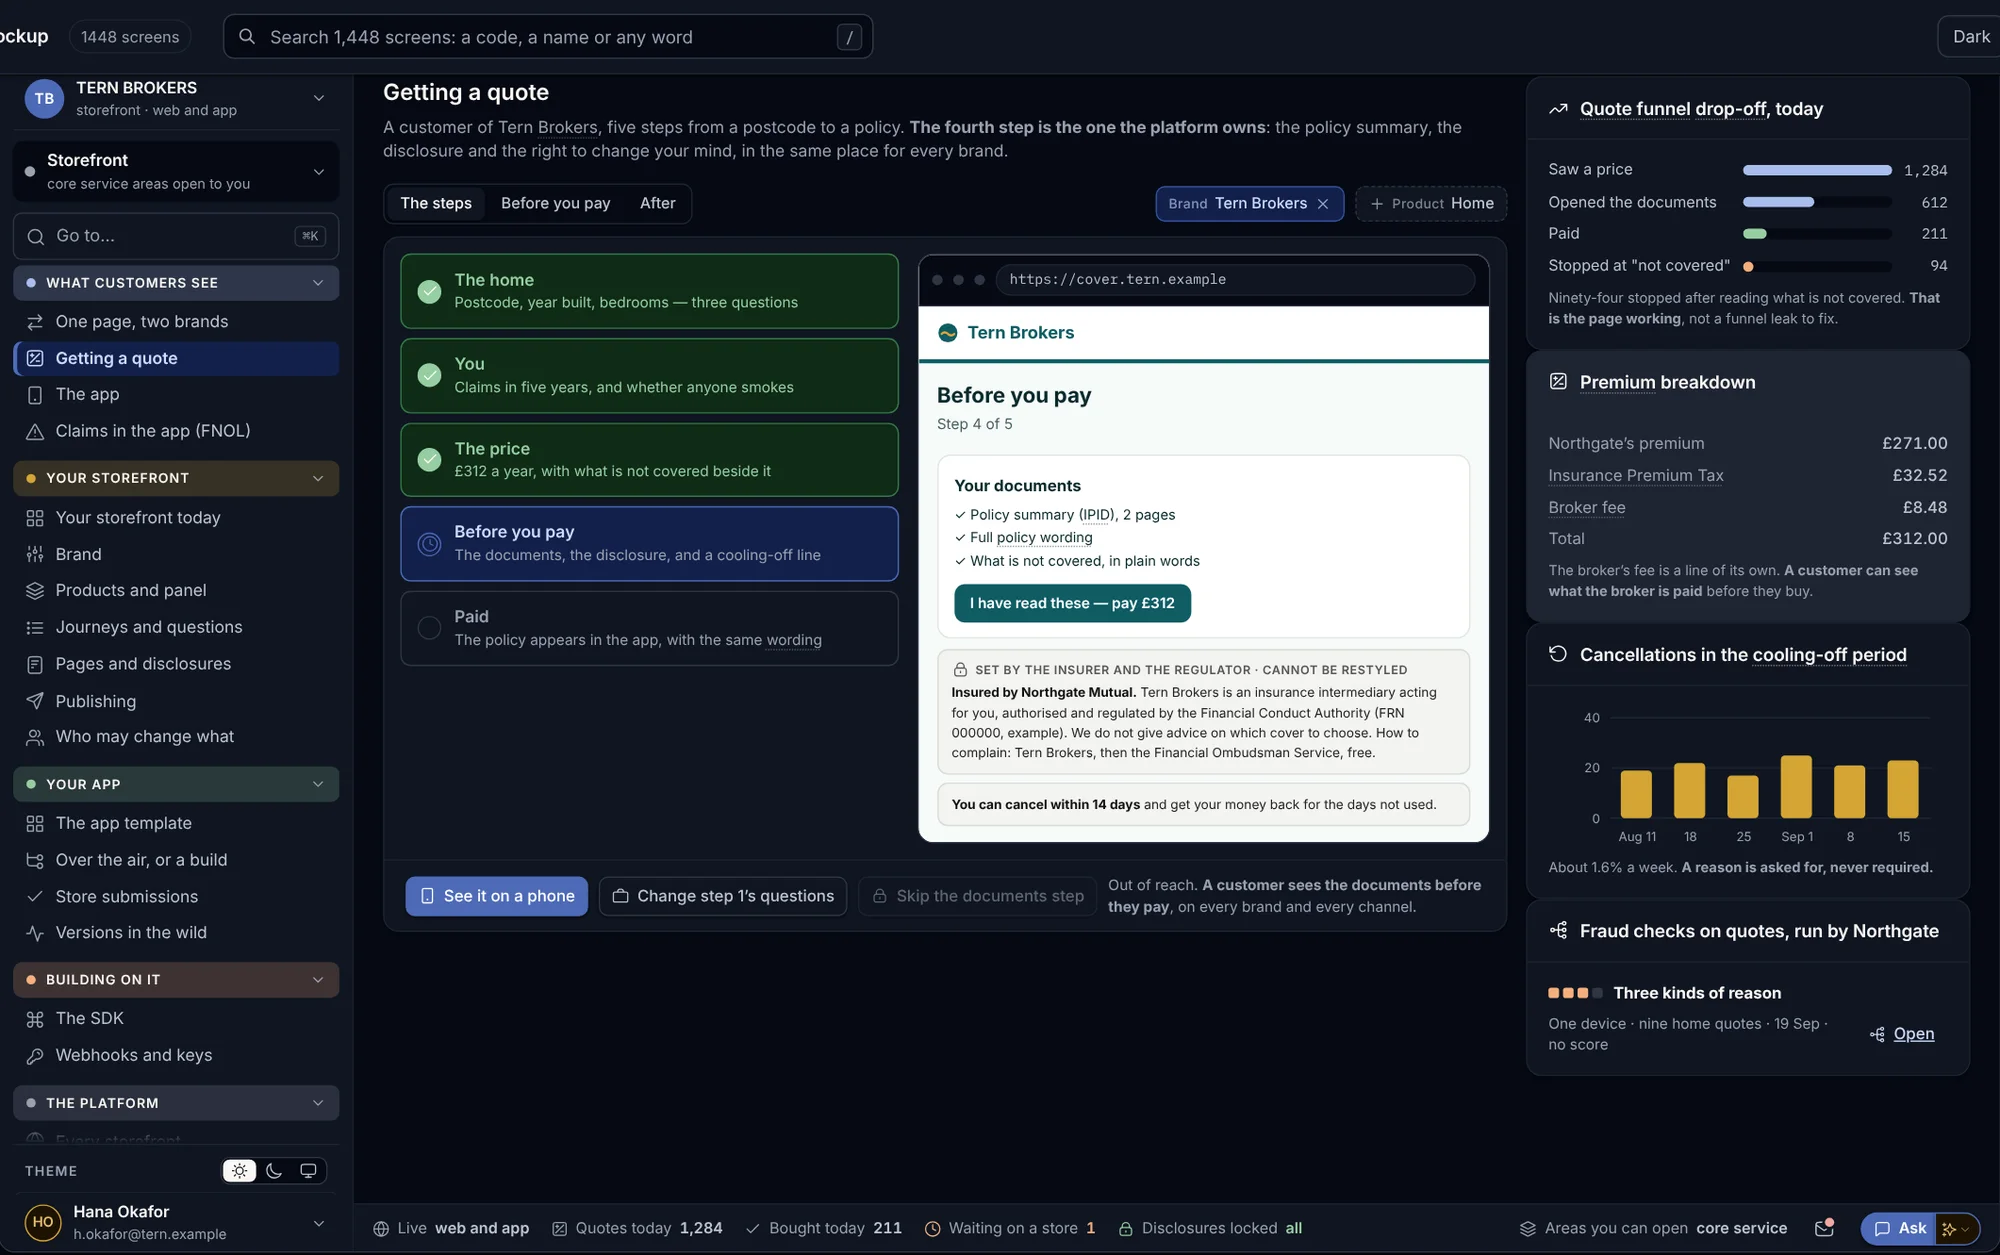
The storefront SDK puts HONESTAS quote, buy and claim journeys on a broker's or insurer's own website and in their own iOS and Android apps. The brand is yours. The documents a customer must see before paying cannot be skipped.
// the storefront SDK for the web, loaded on your page
const quote = storefront.mount("#quote", {
  brand: "tern-brokers",
  product: "home",
  language: "en-IE"
});

quote.on("bound", (policy) => {
  crm.note(policy.id, "Bought online");
});
A branded quote journey, in a few lines
Sandbox access starts with a demo.
We give each team a sandbox firm full of sample claims, policies and records, so you can call every endpoint before you connect a real system.
Book a demo
Tell us what you want to connect: a claims system, a partner, a storefront or your auditor's tools.
Get a sandbox
A sample insurer with its own claims, rooms, refusals and sealed records, and keys that do one job each.
Build against it
The same API, events and webhooks as production, with sample data you can break.
Move to your firm
New keys for your own firm, in our EU cloud or your data centre. Your code does not change.
For developers.
Is there one API for everything?
Yes. Every screen in HONESTAS is built on the same API your systems use, with the same permissions, walls and records. HONESTAS runs on Adverant Nexus, our AI orchestration platform, which is why the API is the same in our EU cloud and in your own data centre.
How do keys work?
Each key belongs to one script or system, may do only the tasks you give it, reaches only the units you choose and ends on a date you set. Every call it makes is recorded, and it can be rotated without downtime.
Can the API write to our claims system?
HONESTAS reads your policy, claims and model systems and never replaces them. When a decision needs writing back, it goes through a checked step that is recorded, never a direct update.
What do refusals look like through the API?
The same codes people see, such as AUTHORITY_EXCEEDED or SCOPE_REFUSED, with a plain reason and the next step. See what it refuses.
Which languages are supported?
The API is plain HTTP and JSON, so any language works. The storefront SDK comes for the web, iOS and Android, and the verifier library for the most common server languages.
Go deeper
Connect your first system.
Bring the system that needs to know when a claim is sealed. We will set up your sandbox and wire the first webhook with you.